

WindTwin-COH
WindTwin Cyber Operations Hub – Operational Resilience Validation Framework for Offshore Wind Essential Entities
Connecting asset exposure, Digital Twin scenario validation, continuous monitoring, SOC investigation, incident response and compliance-ready evidence in one operational resilience workflow for offshore wind environments.
Programme
CYberSynchrony Open Call 1
Duration
8 months
Total budget
€200,000
Coordinator
ZELUS IKE
Partner
Cilix Solutions Ltd
Target maturity
TRL 7
About the project
From cyber exposure to operational readiness
Offshore wind farms operate across tightly connected IT, OT and supplier environments. Remote connectivity, legacy operational technologies and complex multi-vendor supply chains can turn a component vulnerability or configuration weakness into a wider operational risk.
WindTwin-COH addresses this challenge with a repeatable, operationally validated workflow that links hardware and software exposure intelligence to threat and risk scenarios, monitoring priorities, incident response procedures and audit-ready evidence for NIS2-oriented cybersecurity operations.
Asset & supply-chain visibility
Continuous xBOM-driven visibility into hardware, software, dependencies, versions and vulnerability exposure.
Validated cyber readiness
Digital Twin and cyber range execution turns identified risks into realistic scenarios, exercises and measurable preparedness evidence.
Operational evidence
SOC, forensics, monitoring and response outputs are structured into traceable evidence packages supporting NIS2-aligned reporting.
The solution
A sector-specific Cyber Operations Hub
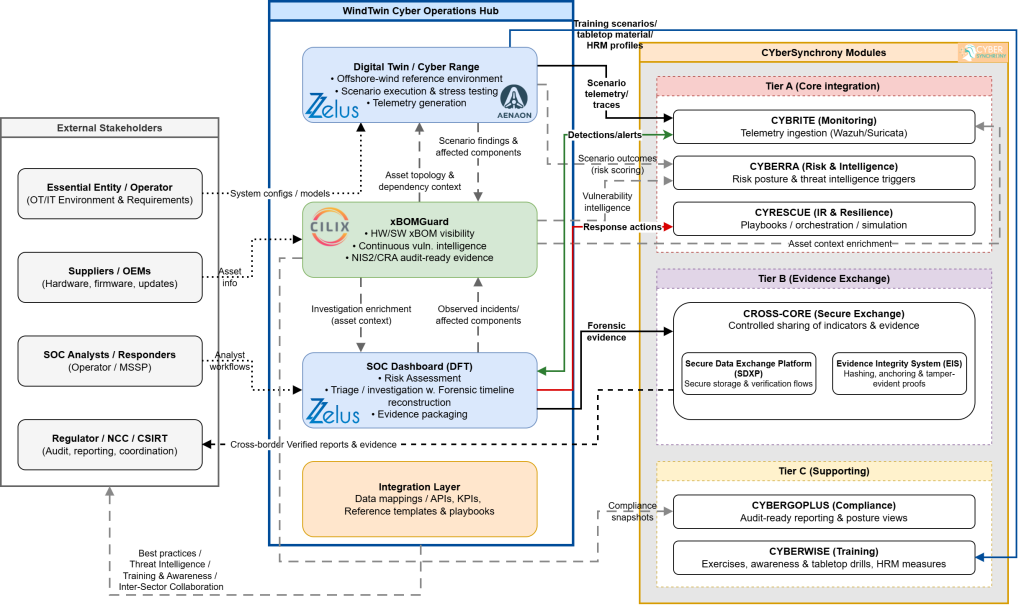
WindTwin-COH brings together mature cybersecurity components into a closed-loop resilience validation framework tailored to offshore wind essential entities.
xBOM intelligence
Continuous HW/SW Bill of Materials visibility and vulnerability/exposure enrichment through CILIX xBOMGuard.
Digital Twin & cyber range
Scenario execution in an offshore-wind-like environment to validate attack paths, impacts, defensive measures and training needs.
Monitoring & correlation
Telemetry and scenario traces are correlated to strengthen detection workflows and support measurable operational monitoring.
SOC, risk & forensics
ZELUS SOC/DFT supports triage, investigation, forensic timeline reconstruction and explicit risk scoring and prioritisation.
Incident response
Validated scenarios trigger response playbooks and exercises, producing evidence of actions, timing and response effectiveness.
Evidence & compliance
Risk snapshots, incident timelines, monitoring artefacts and scenario logs are packaged for controlled sharing and audit readiness.
Specific objectives
Four objectives, one integrated workflow
Sector-specific Cyber Operations Hub
Deploy an operational hub combining Digital Twin readiness, xBOM visibility, monitoring, SOC triage, forensics, risk assessment and incident-response orchestration for offshore wind OT/IT and supplier environments.
Enhanced threat intelligence & risk assessment
Turn xBOM-derived exposures into repeatable offshore-wind threat and risk scenarios, validate them in the Digital Twin and convert findings into risk posture updates and response priorities.
Awareness & training
Transform scenario execution and response lessons into cyber range sessions, tabletop exercises and concise operator playbooks for OT/IT and supplier-facing roles.
Cross-sector replication
Package evidence structures, templates and mappings so the approach can be transferred to other NIS2 sectors such as water, transport and manufacturing.
Operational workflow
How WindTwin-COH works
The project follows a closed loop from asset intelligence to validated resilience outcomes and evidence.
Discover exposures
xBOMGuard maps components, dependencies, versions and vulnerabilities.
Define scenarios
Exposure intelligence is translated into candidate threat and risk scenarios.
Execute in the Twin
Scenarios are run in the Digital Twin/cyber range to validate feasibility and impact.
Monitor & correlate
Telemetry and scenario traces feed detection, triage and KPI measurement.
Assess & investigate
SOC/DFT workflows create risk posture updates and forensic timelines.
Validate response
Response playbooks are executed and measured through scenario-driven exercises.
Package evidence
Outputs are prepared for controlled sharing, compliance and replication.
Measured impact
Key project targets
WindTwin-COH is designed around measurable operational, technical, training and compliance outcomes.
≥2
offshore wind essential entities supported, with a target of 3
≥12
threat assessments and risk scenario analyses
≥2
risk monitoring services producing periodic posture updates
≥30
participants reached through cyber range and tabletop training
≥85%
xBOM coverage of assets/components with vulnerability enrichment
≥20%
scenario-based improvement target for detection contextualisation
≥15%
scenario-based improvement target for incident response time
≥80%
evidence completeness for the selected NIS2/CRA control set
Implementation
Eight-month delivery plan
The work plan moves from baseline architecture to an integrated MVP, operational validation, training and a final TRL 7 demonstration.
Setup & baseline
Reference environment, requirements, KPI instrumentation and evidence formats.
Operational Hub integration
Digital Twin telemetry, SOC/DFT, xBOMGuard, monitoring and evidence exchange.
Threat & risk monitoring
xBOM-driven intelligence, scenario library, assessments and ongoing risk monitoring.
Incident response validation
Playbook integration and procedural validation through Digital Twin exercises.
Training & final demo
Cyber range sessions, awareness, replication toolkit and final demonstration.
Expected impact
Resilience that can be tested, measured and reused
Technical
Reduced visibility gaps, validated detection logic, evidence-grade investigations and explicit risk prioritisation.
Operational
Faster repeatable assessments, exercised incident procedures and practical readiness for offshore wind operators.
Compliance
Traceable evidence connecting asset exposure to mitigation, incident handling and NIS2-oriented reporting.
Cross-sector
Reusable templates and evidence structures designed for transfer to other NIS2 critical sectors.
Consortium
Two complementary cybersecurity SMEs
Coordinator · Greece
ZELUS IKE
ZELUS leads overall coordination, system-level integration, the Digital Twin and cyber range environment, SOC/DFT investigation workflows, risk assessment, KPI evidence packaging, training and the final end-to-end demonstration.
Partner · Cyprus
Cilix Solutions Ltd
Cilix leads xBOMGuard integration, continuous vulnerability/exposure enrichment, threat and risk scenario inputs, monitoring support and incident-response/playbook integration, while contributing to replication and training materials.
European cybersecurity ecosystem
Built on existing assets and connected to CYberSynchrony
WindTwin-COH integrates with CYberSynchrony modules for monitoring, threat/risk analysis, incident response, secure exchange, training and compliance structuring.
- CYBRITE · Monitoring
- CYBERRA · Threat/Risk
- CYRESCUE · Incident Response
- CROSS-CORE · Secure Exchange
- CYBERWISE · Training
- CYBERGOPLUS · Compliance
- Key Concepts: Food waste, Packaging, SME uptake
- Website: https://circularis-heu.eu/
- Duration: 48 Months
- Start Date: 1/5/2026
